ISO/IEC 19772:2009 PDF
Information technology — Security techniques — Authenticated encryption
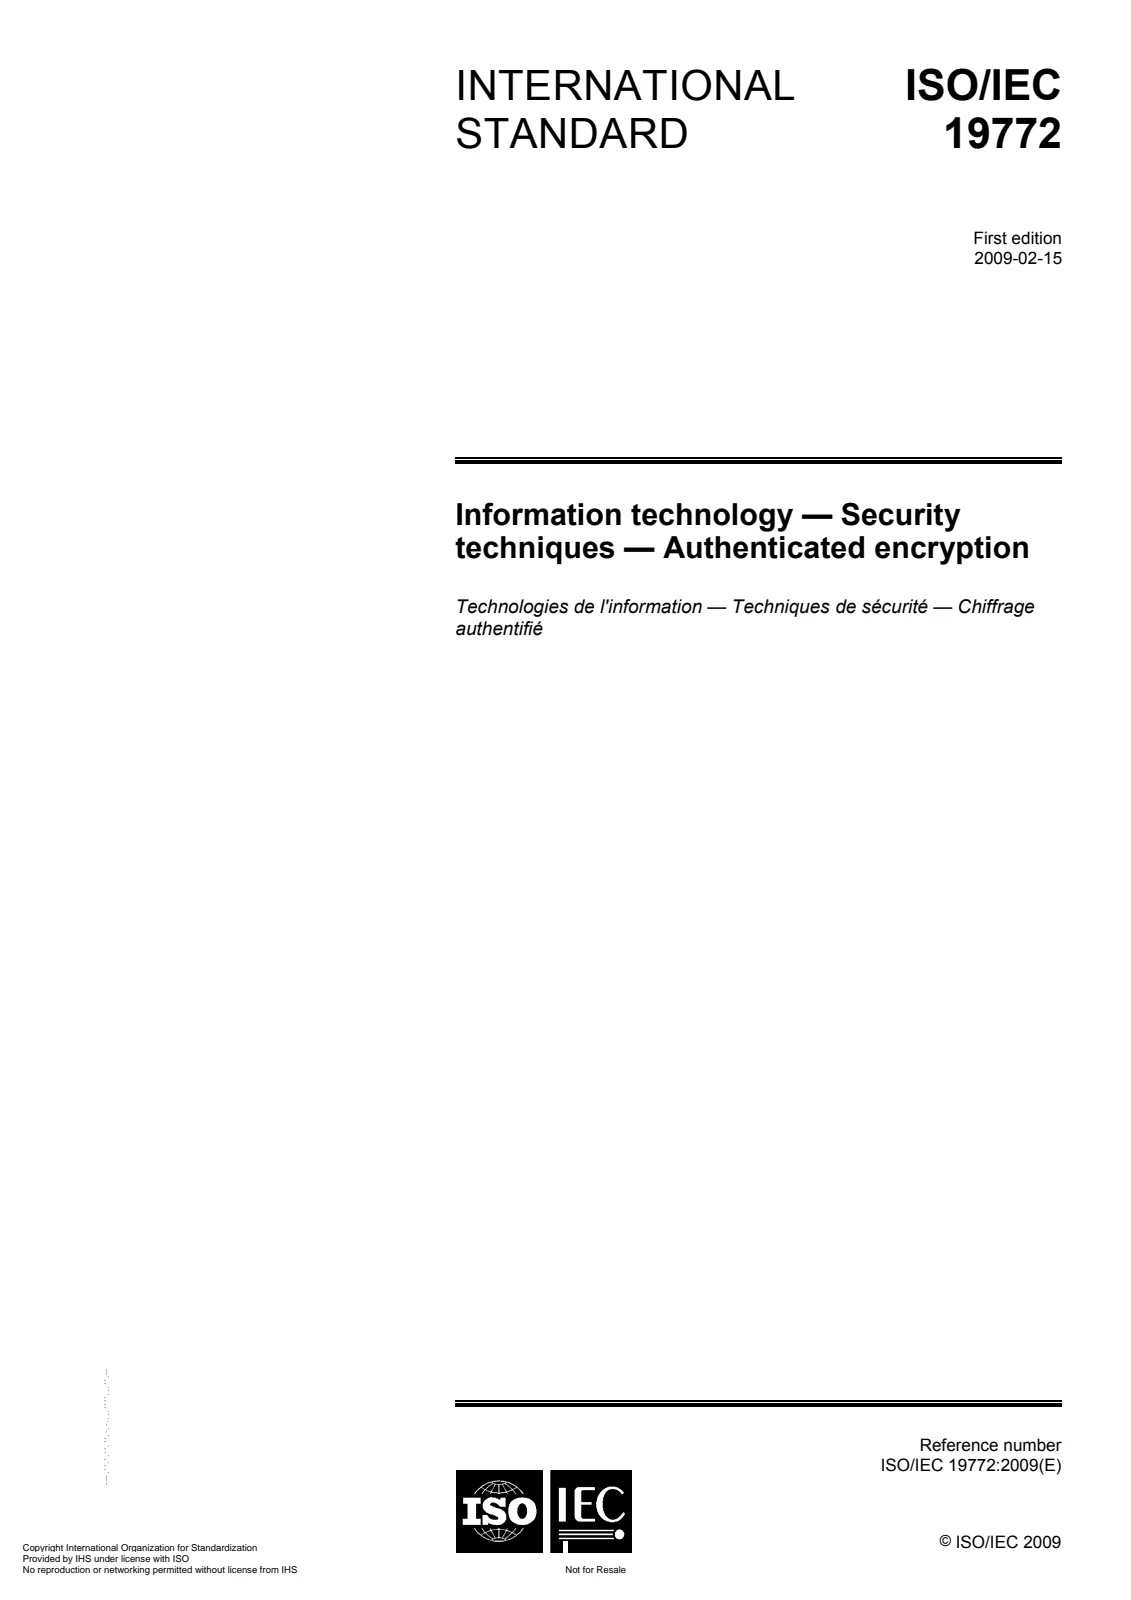
Information technology — Security techniques — Authenticated encryption
- Document status:
- Withdrawn
- Format:
- Electronic (PDF)
- Number of pages:
- 29
- Publication date:
- February 12, 2009
- Edition:
- ISO/IEC IS 19772 edition 1 version 1
- ICS:
- 35.030
ISO/IEC 19772:2009 specifies six methods for authenticated encryption, i.e. defined ways of processing a data string with the following security objectives: data confidentiality, i.e. protection against unauthorized disclosure of data; data integrity, i.e. protection that enables the recipient of data to verify that it has not been modified; data origin authentication, i.e. protection that enables the recipient of data to verify the identity of the data originator. All six methods specified in ISO/IEC 19772:2009 require the originator and the recipient of the protected data to share a secret key. Key management is outside the scope of ISO/IEC 19772:2009; key management techniques are defined in ISO/IEC 11770.
Technical details
- Technical committee
- ISO/IEC JTC 1/SC 27 - Information security, cybersecurity and privacy protection
- SKU
- ISO/IEC 19772:2009