ISO/IEC 19790:2012 PDF
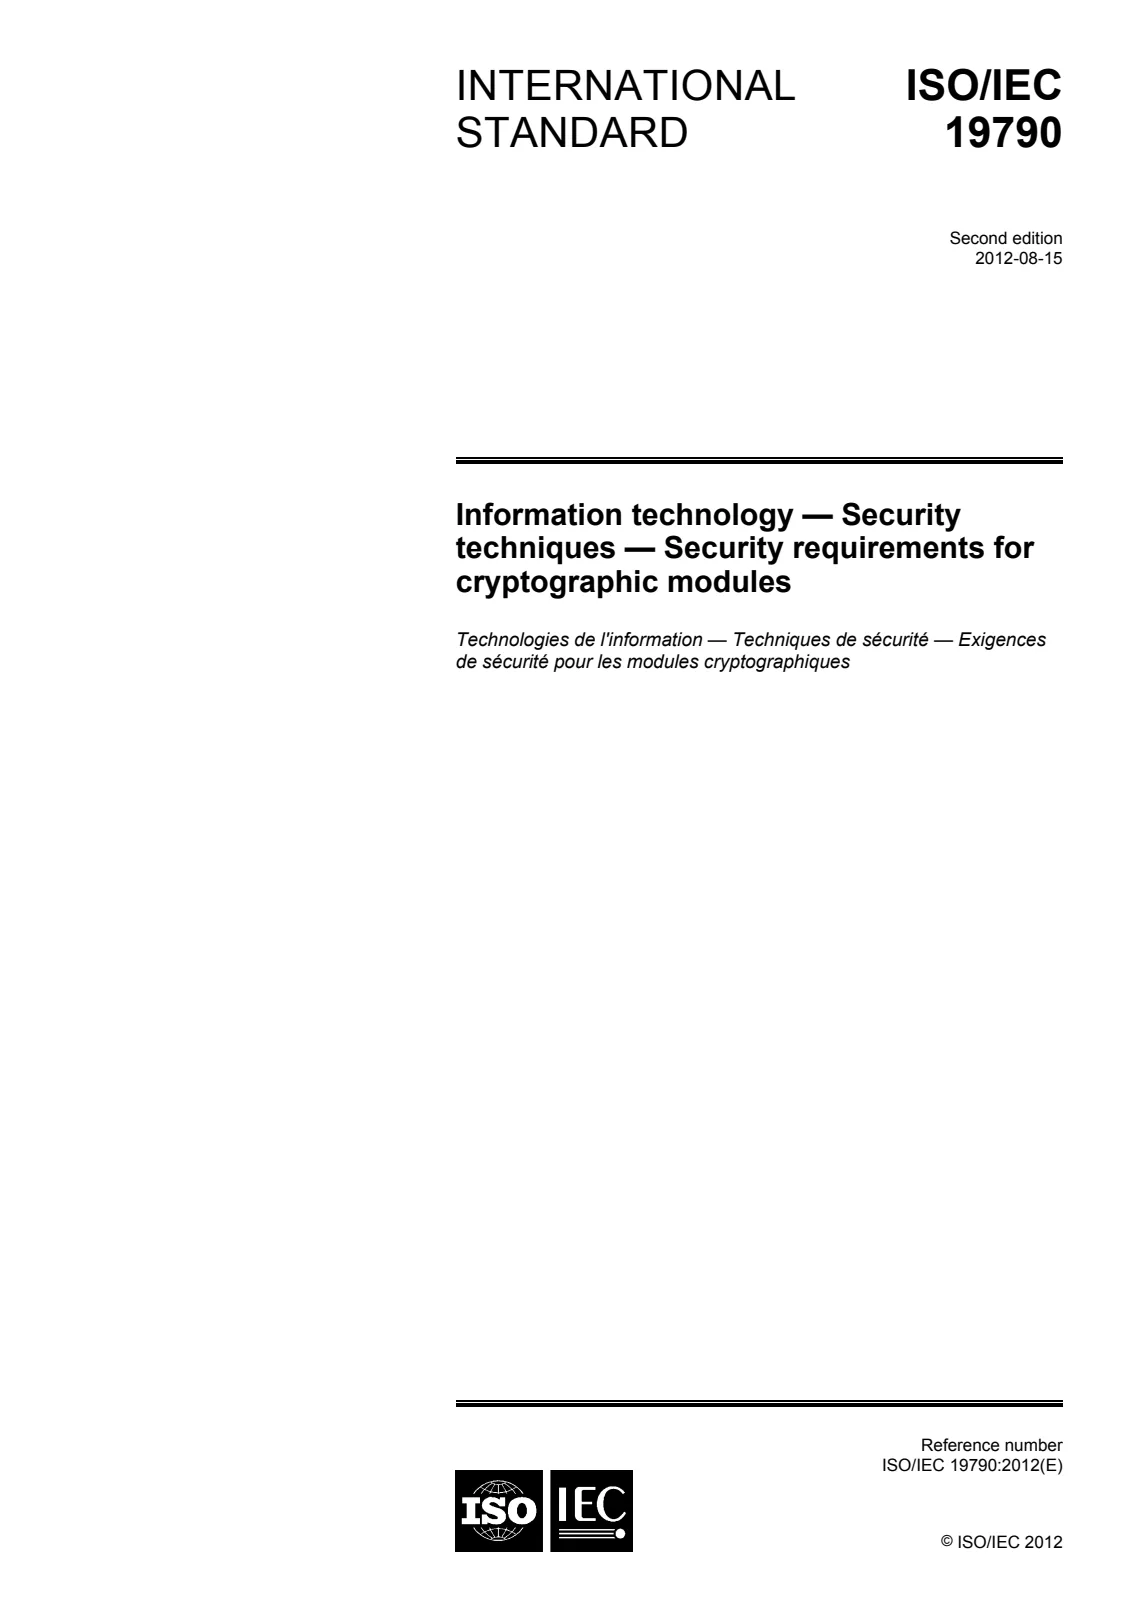
Information technology — Security techniques — Security requirements for cryptographic modules
 Open preview (PDF)Information technology — Security techniques — Security requirements for cryptographic modules
Information technology — Security techniques — Security requirements for cryptographic modules
- Document status:
- Withdrawn
- Format:
- Electronic (PDF)
- Number of pages:
- 72
- Publication date:
- August 9, 2012
- Edition:
- ISO/IEC IS 19790 edition 2 version 1
- ICS:
- 35.030
ISO/IEC 19790:2012 the security requirements for a cryptographic module utilised within a security system protecting sensitive information in computer and telecommunication systems. This International Standard defines four security levels for cryptographic modules to provide for a wide spectrum of data sensitivity (e.g. low value administrative data, million dollar funds transfers, life protecting data, personal identity information, and sensitive information used by government) and a diversity of application environments (e.g. a guarded facility, an office, removable media, and a completely unprotected location). This International Standard specifies four security levels for each of 11 requirement areas with each security level increasing security over the preceding level. ISO/IEC 19790:2012 specifies security requirements specifically intended to maintain the security provided by a cryptographic module and compliance with this International Standard is not sufficient to ensure that a particular module is secure or that the security provided by the module is sufficient and acceptable to the owner of the information that is being protected.
Technical details
- Technical committee
- ISO/IEC JTC 1/SC 27 - Information security, cybersecurity and privacy protection
- SKU
- ISO/IEC 19790:2012