ISO/IEC 27009:2020 PDF
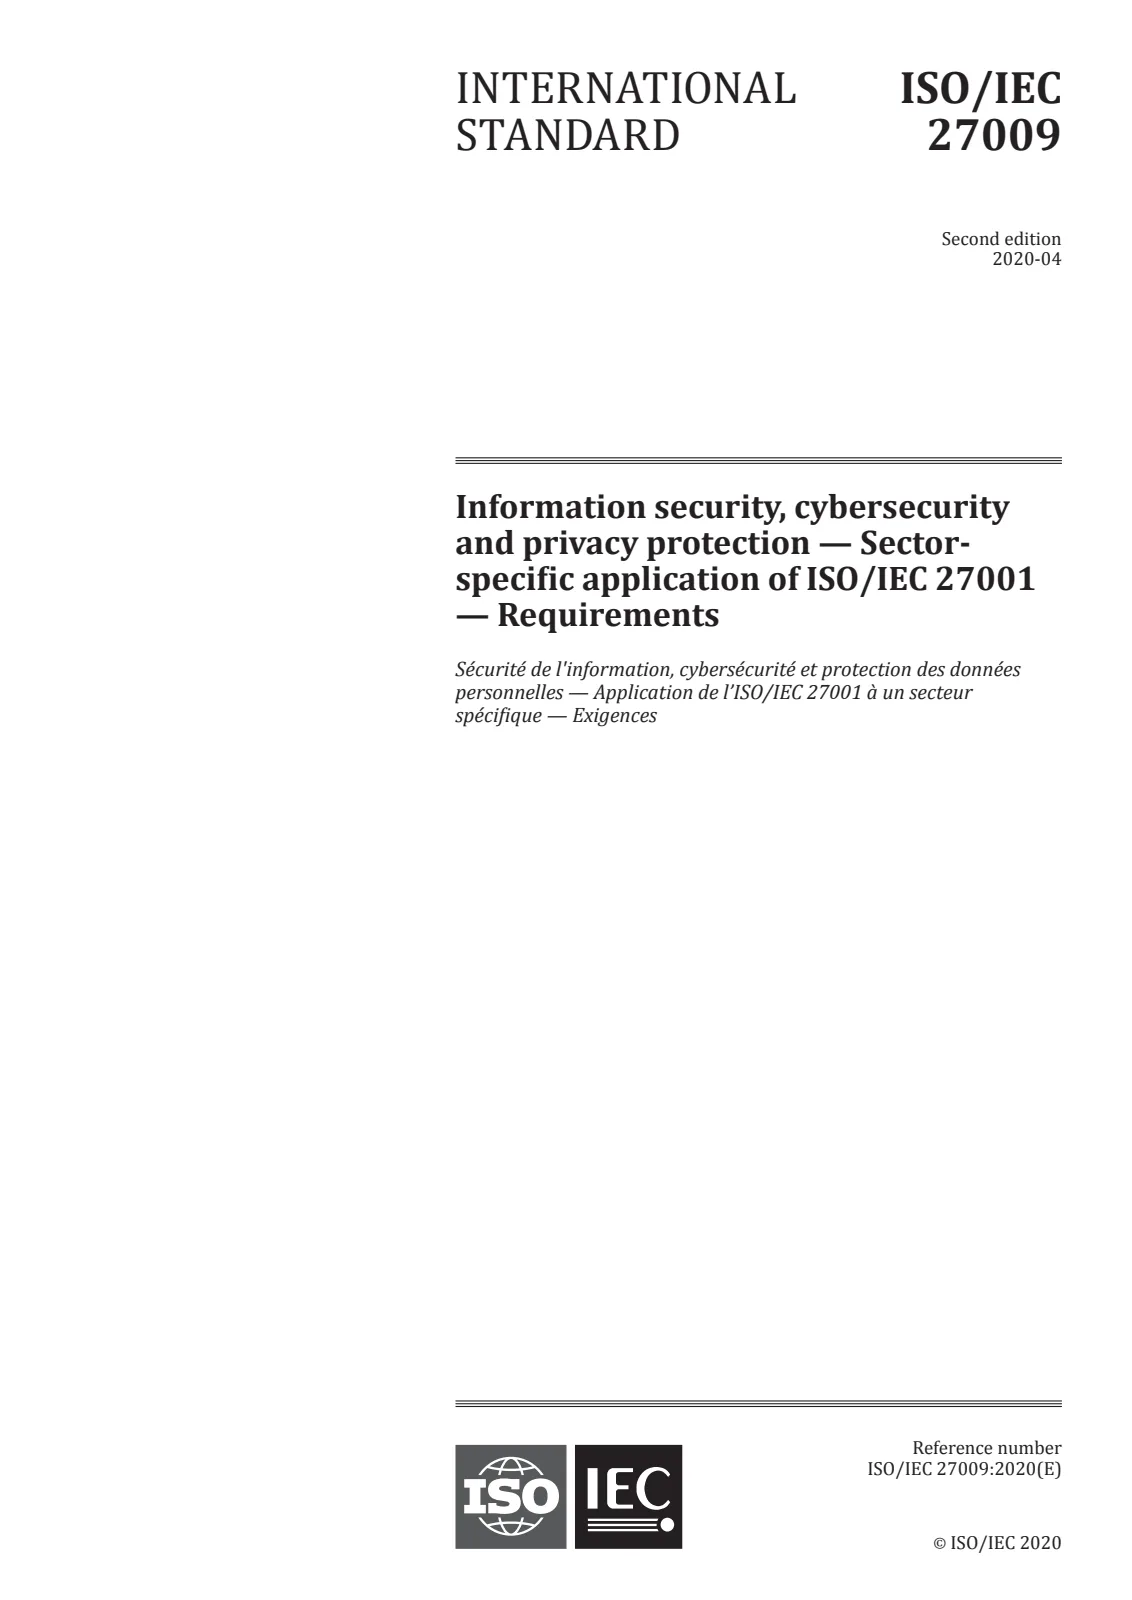
Information security, cybersecurity and privacy protection — Sector-specific application of ISO/IEC 27001 — Requirements
 Open preview (PDF)Information security, cybersecurity and privacy protection — Sector-specific application of ISO/IEC 27001 — Requirements
Information security, cybersecurity and privacy protection — Sector-specific application of ISO/IEC 27001 — Requirements
- Document status:
- Withdrawn
- Format:
- Electronic (PDF)
- Number of pages:
- 18
- Publication date:
- April 21, 2020
- Edition:
- ISO/IEC IS 27009 edition 2 version 1
- ICS:
- 03.100.70
This document specifies the requirements for creating sector-specific standards that extend ISO/IEC 27001, and complement or amend ISO/IEC 27002 to support a specific sector (domain, application area or market). This document explains how to: — include requirements in addition to those in ISO/IEC 27001, — refine or interpret any of the ISO/IEC 27001 requirements, — include controls in addition to those of ISO/IEC 27001:2013, Annex A and ISO/IEC 27002, — modify any of the controls of ISO/IEC 27001:2013, Annex A and ISO/IEC 27002, — add guidance to or modify the guidance of ISO/IEC 27002. This document specifies that additional or refined requirements do not invalidate the requirements in ISO/IEC 27001. This document is applicable to those involved in producing sector-specific standards.
Technical details
- Technical committee
- ISO/IEC JTC 1/SC 27 - Information security, cybersecurity and privacy protection
- SKU
- ISO/IEC 27009:2020