ISO/IEC 27013:2015 PDF
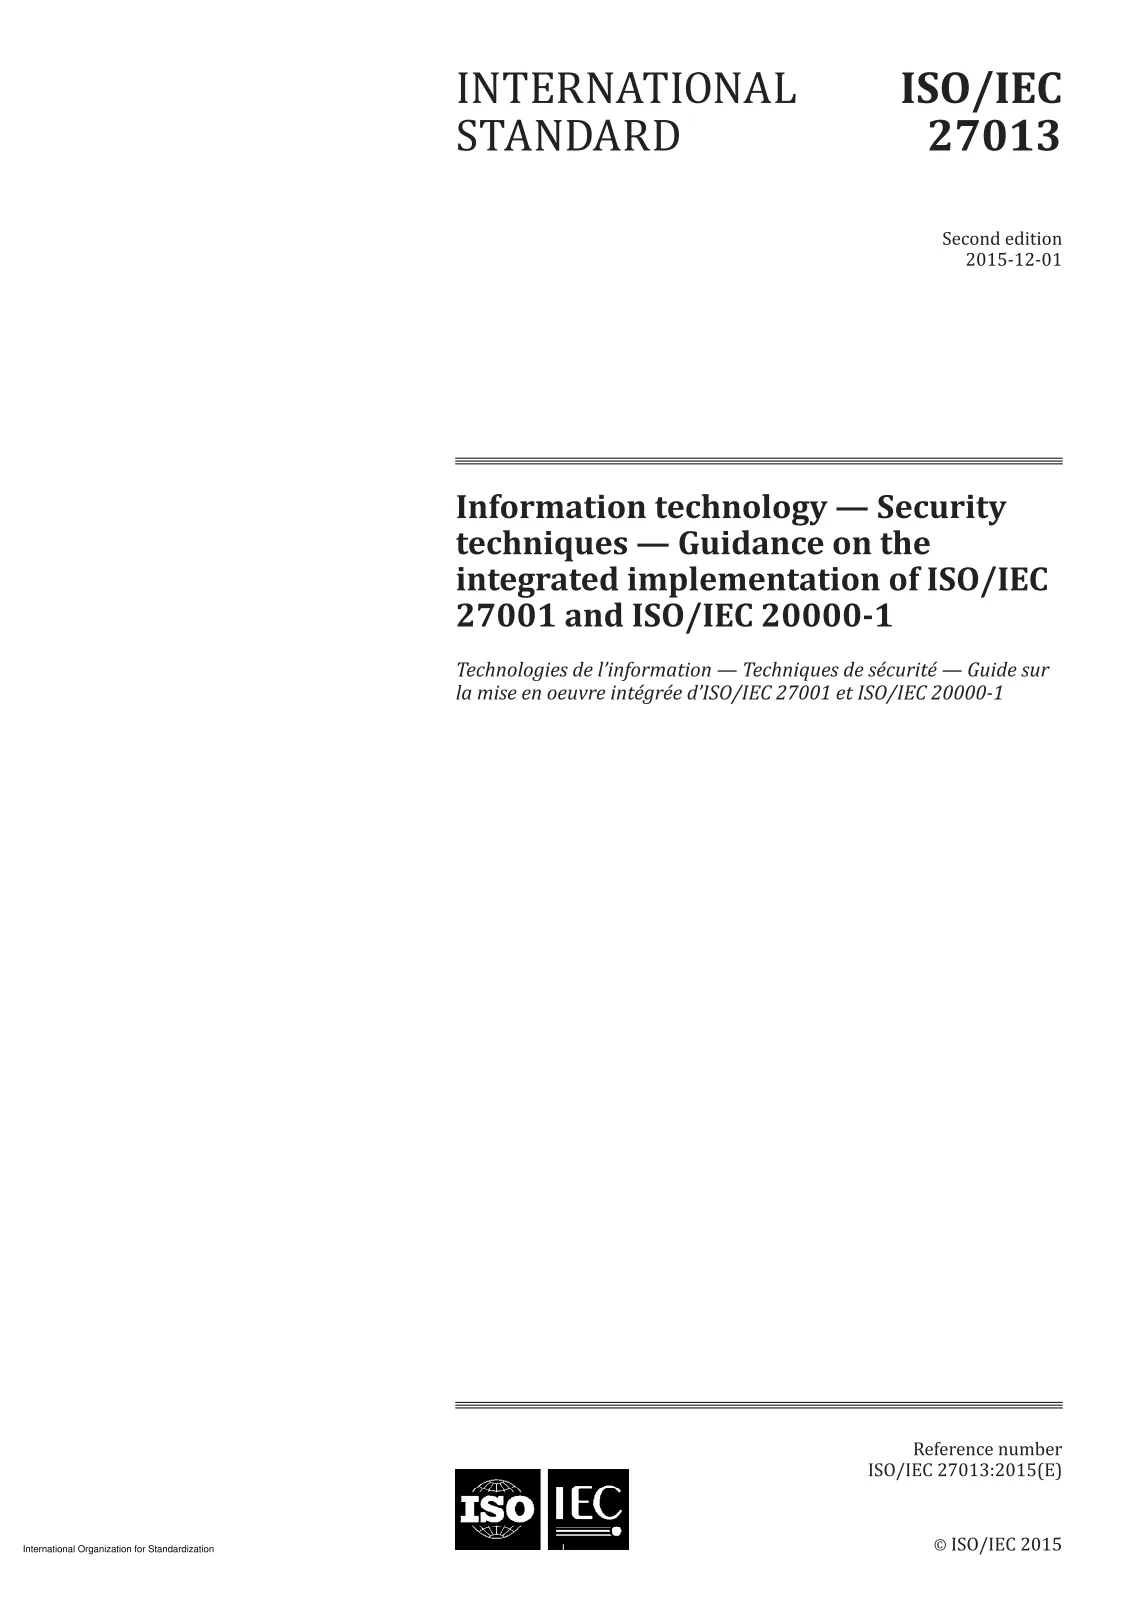
Information technology — Security techniques — Guidance on the integrated implementation of ISO/IEC 27001 and ISO/IEC 20000-1
 Open preview (PDF)Information technology — Security techniques — Guidance on the integrated implementation of ISO/IEC 27001 and ISO/IEC 20000-1
Information technology — Security techniques — Guidance on the integrated implementation of ISO/IEC 27001 and ISO/IEC 20000-1
- Document status:
- Withdrawn
- Format:
- Electronic (PDF)
- Number of pages:
- 39
- Publication date:
- November 24, 2015
- Edition:
- ISO/IEC IS 27013 edition 2 version 1
- ICS:
- 03.080.99
ISO/IEC 27013:2015 provides guidance on the integrated implementation of ISO/IEC 27001 and ISO/IEC 20000‑1 for those organizations that are intending to either a) implement ISO/IEC 27001 when ISO/IEC 20000‑1 is already implemented, or vice versa, b) implement both ISO/IEC 27001 and ISO/IEC 20000‑1 together, or c) integrate existing management systems based on ISO/IEC 27001 and ISO/IEC 20000‑1. ISO/IEC 27013:2015 focuses exclusively on the integrated implementation of an information security management system (ISMS) as specified in ISO/IEC 27001 and a service management system (SMS) as specified in ISO/IEC 20000‑1. In practice, ISO/IEC 27001 and ISO/IEC 20000‑1 can also be integrated with other management system standards, such as ISO 9001 and ISO 14001.
Technical details
- Technical committee
- ISO/IEC JTC 1/SC 27 - Information security, cybersecurity and privacy protection
- SKU
- ISO/IEC 27013:2015