ISO/IEC 27036-2:2014 PDF
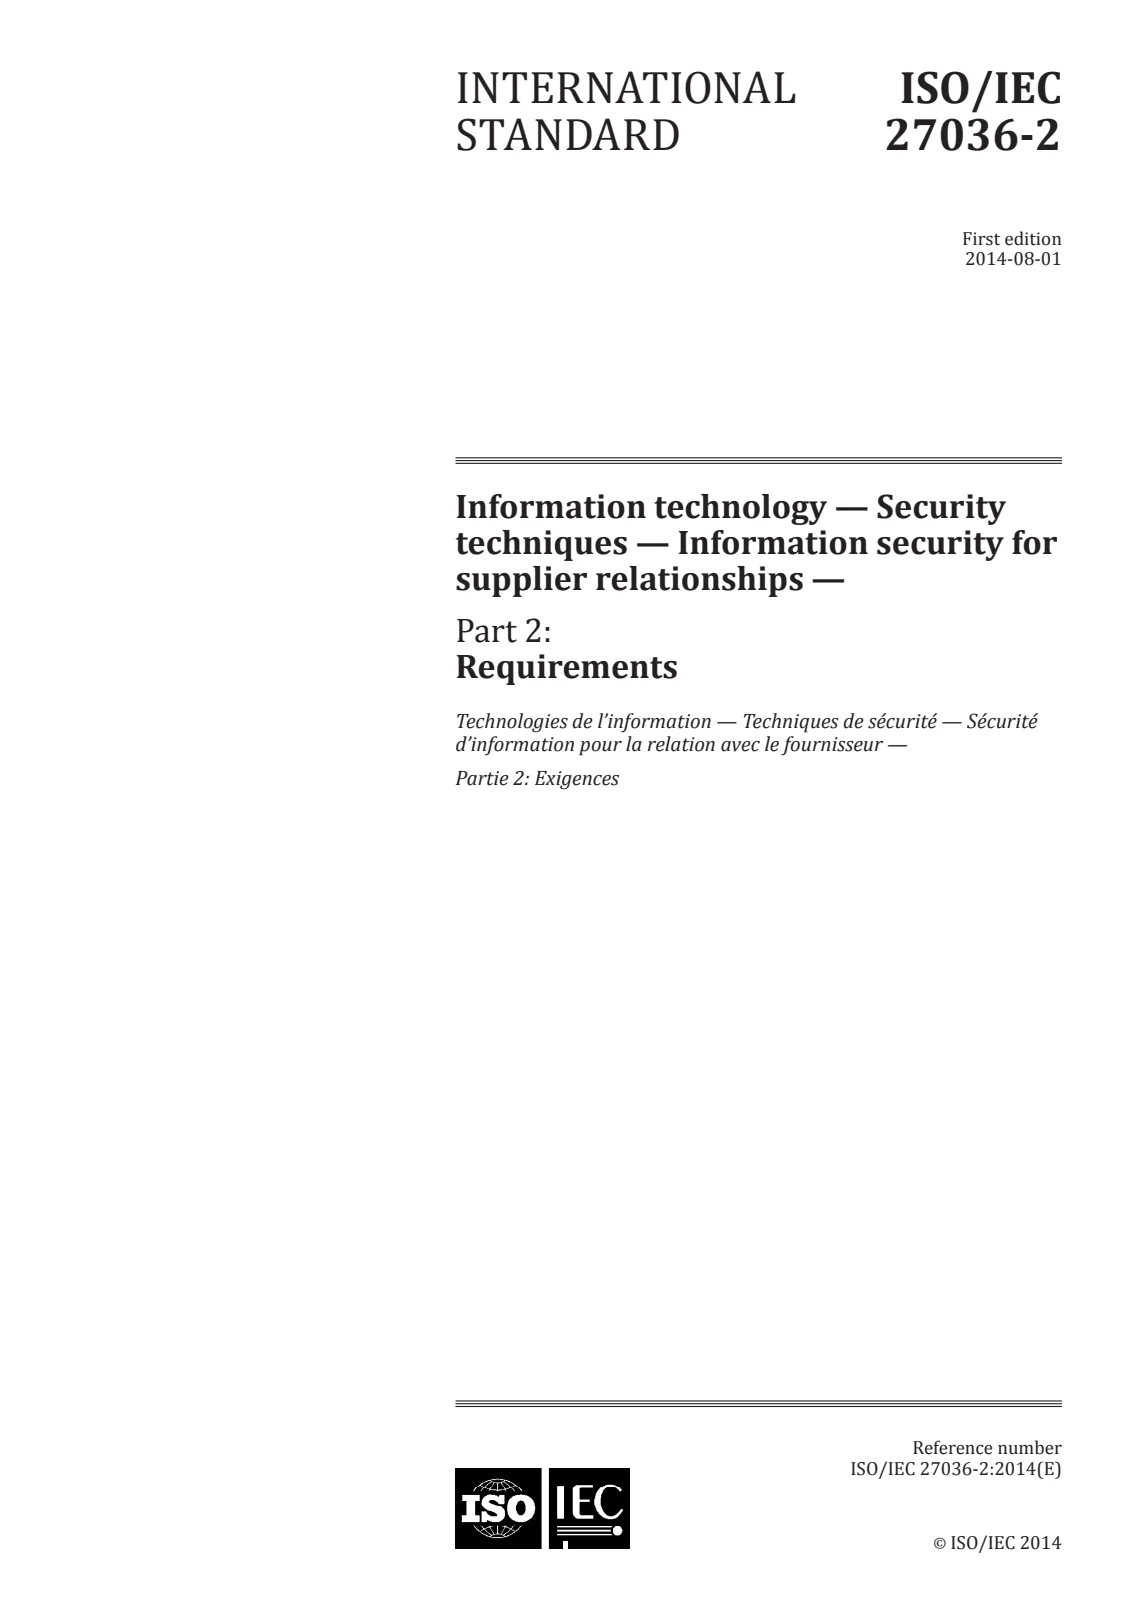
Information technology — Security techniques — Information security for supplier relationships — Part 2: Requirements
 Open preview (PDF)Information technology — Security techniques — Information security for supplier relationships — Part 2: Requirements
Information technology — Security techniques — Information security for supplier relationships — Part 2: Requirements
- Document status:
- Withdrawn
- Format:
- Electronic (PDF)
- Number of pages:
- 38
- Publication date:
- July 25, 2014
- Edition:
- ISO/IEC IS 27036 edition 1 version 1
- ICS:
- 35.030
ISO/IEC 27036-2:2014 specifies fundamental information security requirements for defining, implementing, operating, monitoring, reviewing, maintaining and improving supplier and acquirer relationships. These requirements cover any procurement and supply of products and services, such as manufacturing or assembly, business process procurement, software and hardware components, knowledge process procurement, Build-Operate-Transfer and cloud computing services. These requirements are intended to be applicable to all organizations, regardless of type, size and nature. To meet these requirements, an organization should have already internally implemented a number of foundational processes, or be actively planning to do so. These processes include, but are not limited to, the following: governance, business management, risk management, operational and human resources management, and information security.
Technical details
- Technical committee
- ISO/IEC JTC 1/SC 27 - Information security, cybersecurity and privacy protection
- SKU
- ISO/IEC 27036-2:2014