ISO/IEC TR 20004:2012 PDF
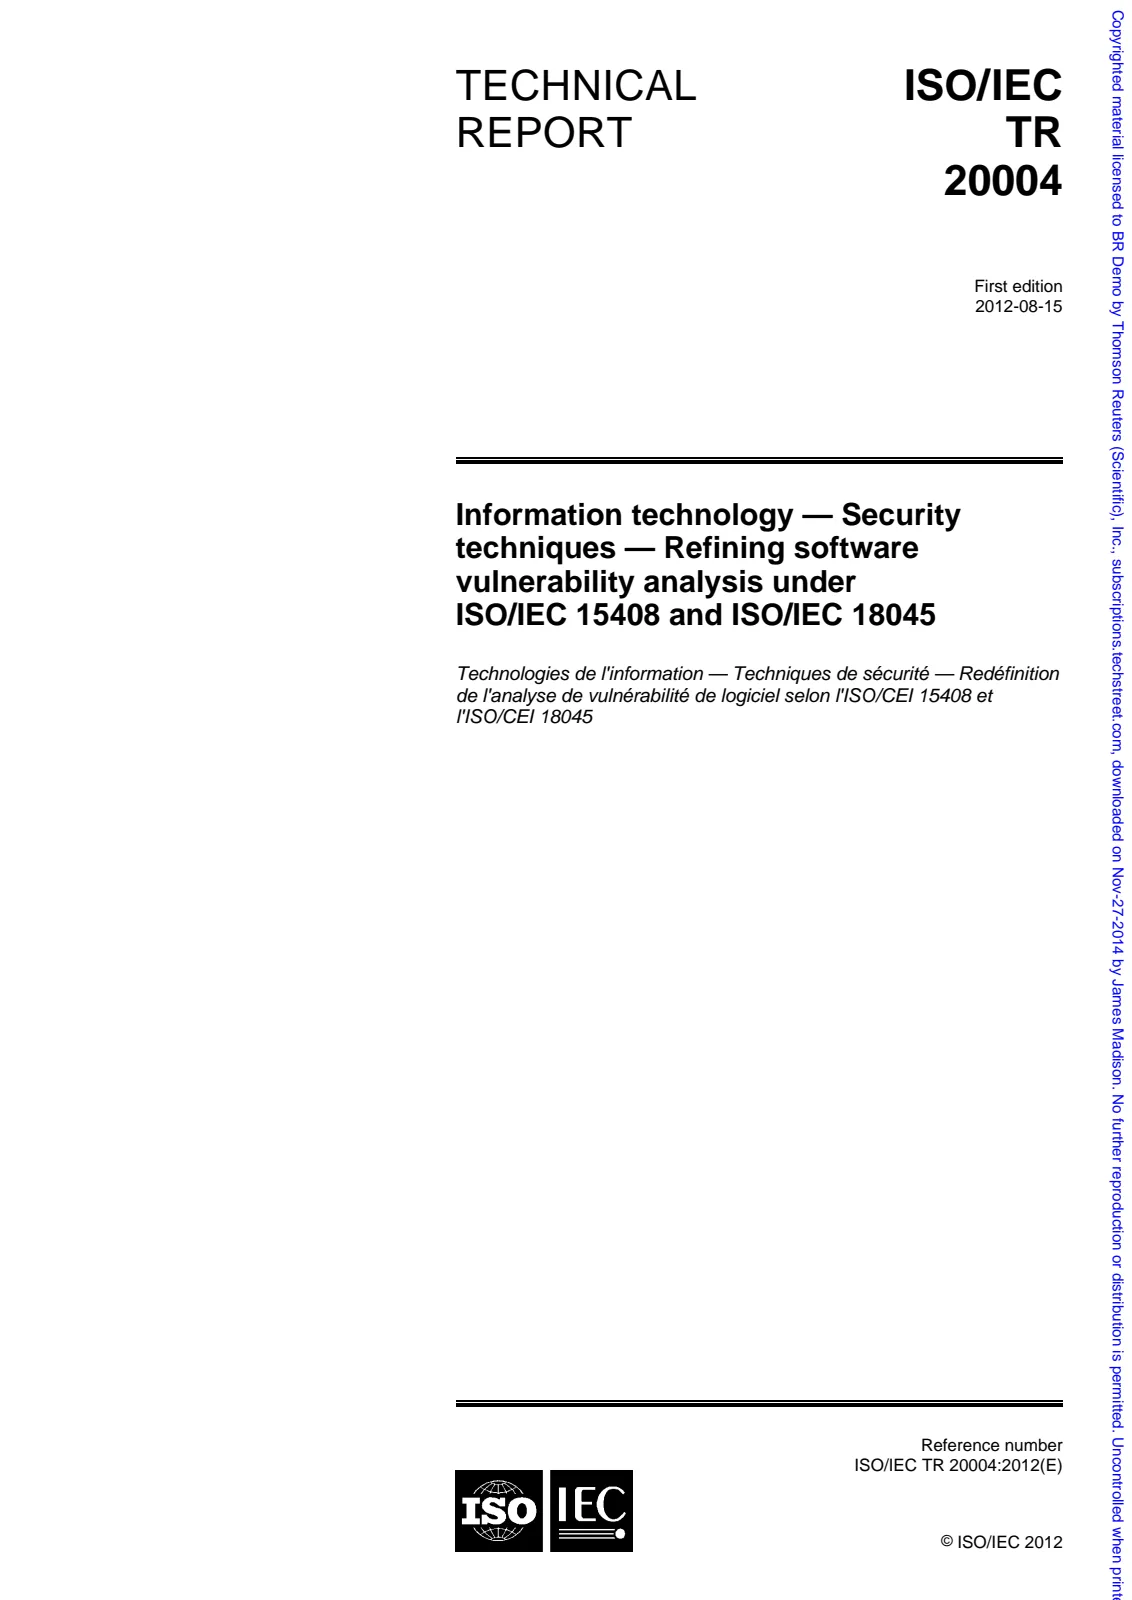
Information technology — Security techniques — Refining software vulnerability analysis under ISO/IEC 15408 and ISO/IEC 18045
 Open preview (PDF)Information technology — Security techniques — Refining software vulnerability analysis under ISO/IEC 15408 and ISO/IEC 18045
Information technology — Security techniques — Refining software vulnerability analysis under ISO/IEC 15408 and ISO/IEC 18045
- Document status:
- Withdrawn
- Format:
- Electronic (PDF)
- Number of pages:
- 17
- Publication date:
- August 8, 2012
- Edition:
- ISO/IEC TR 20004 edition 1 version 1
- ICS:
- 35.030
ISO/IEC TR 20004:2012 refines the AVA_VAN assurance family activities defined in ISO/IEC 18045:2008 and provides more specific guidance on the identification, selection and assessment of relevant potential vulnerabilities in order to conduct an ISO/IEC 15408 evaluation of a software target of evaluation. ISO/IEC TR 20004:2012 leverages the Common Weakness Enumeration (CWE) and the Common Attack Pattern Enumeration and Classification (CAPEC) to support the method of scoping and implementing ISO/IEC 18045:2008(E) vulnerability analysis activities. ISO/IEC TR 20004:2012 does not define evaluator actions for certain high assurance ISO/IEC 15408 components, where there is as yet no generally agreed guidance.
Technical details
- Technical committee
- ISO/IEC JTC 1/SC 27 - Information security, cybersecurity and privacy protection
- SKU
- ISO/IEC TR 20004:2012